Dozens of credit unions alerted to potential data breach following cyberattack
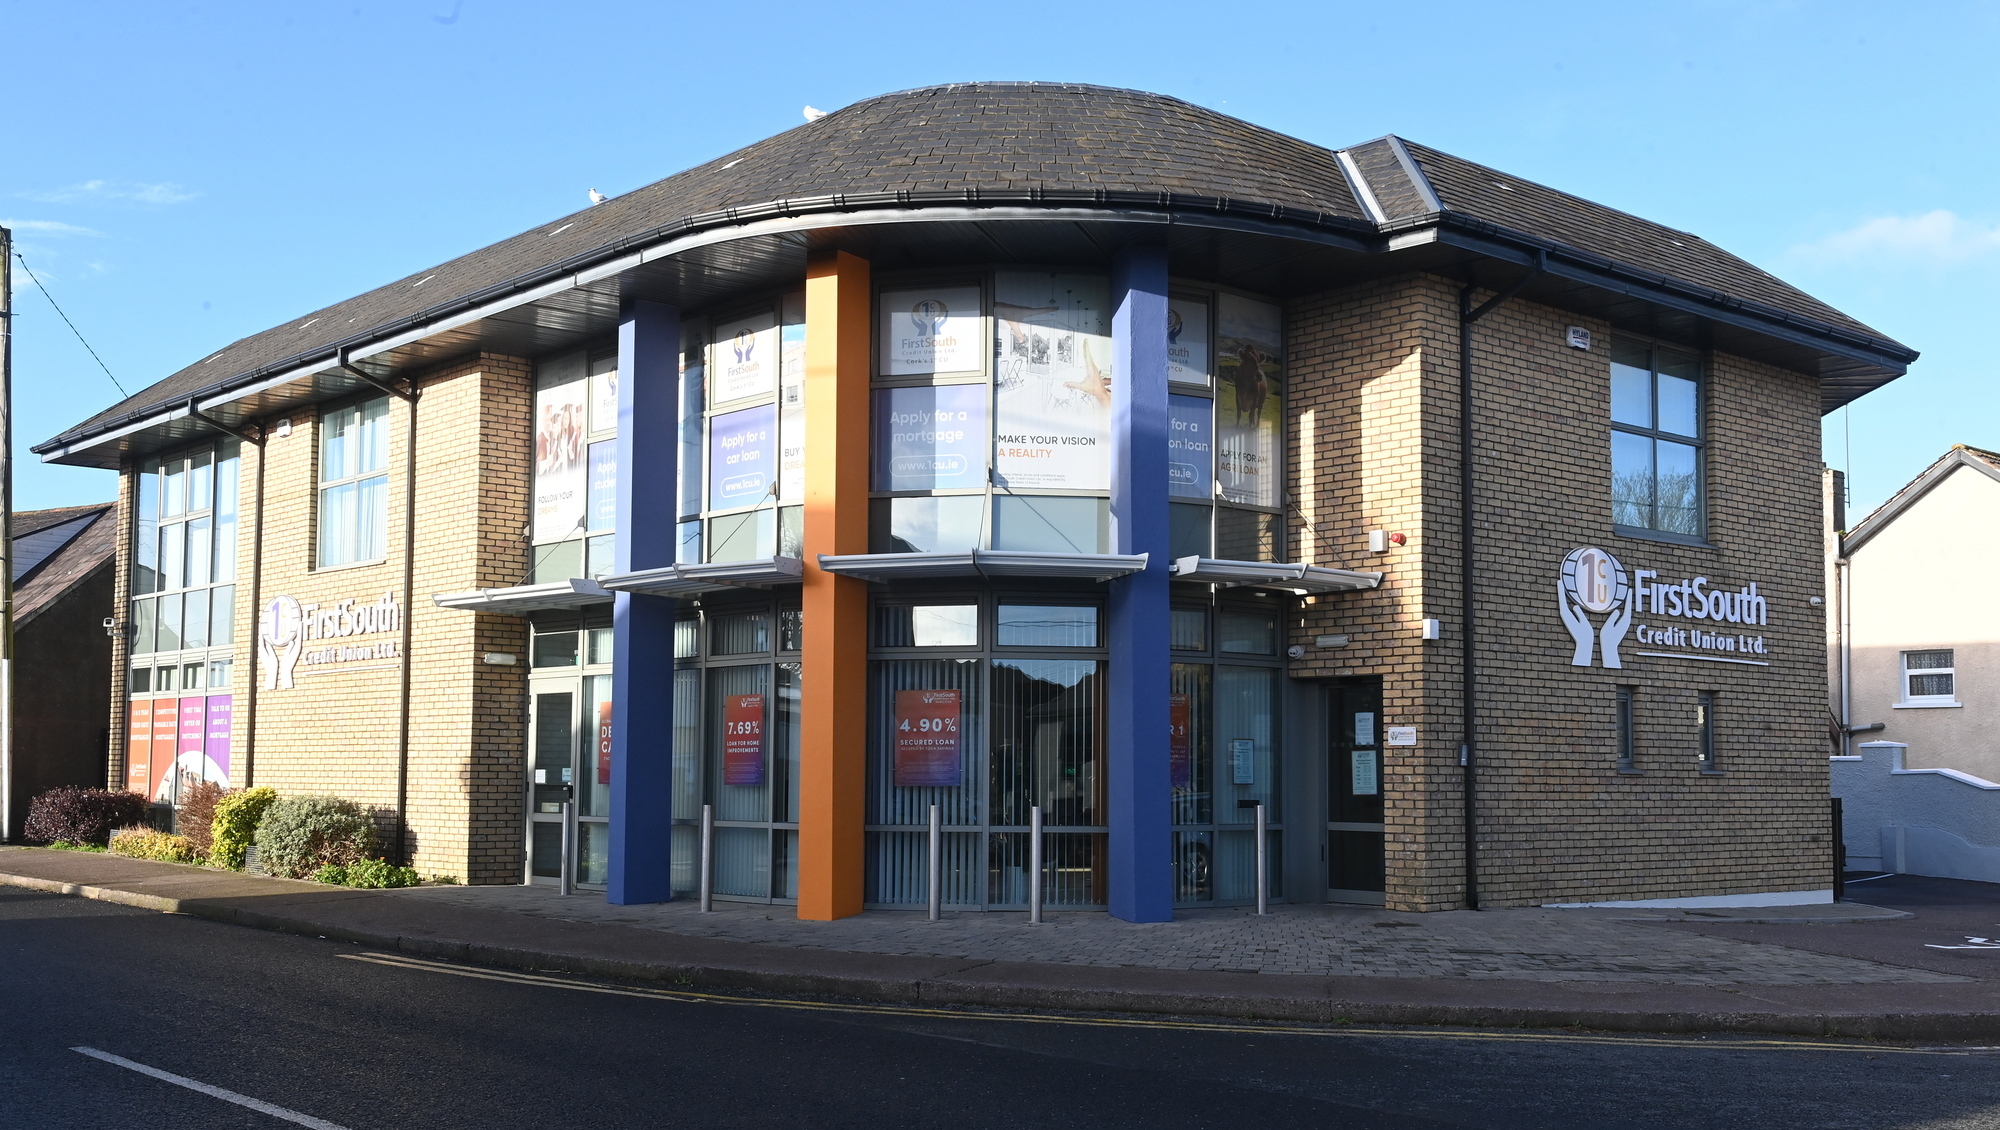
The Department of Finance said a 'limited' number of credit unions had been affected by the potential breach. File picture: Larry Cummins
Several data breach reports have been made to the regulator after a flaw in software used by dozens of credit unions was exploited last month.
The Data Protection Commission said it had received "a number of breach notifications" from credit unions and was contacting the relevant parties "as a matter of priority".
A company providing banking software services to credit unions said the potential breach posed a risk of financial fraud, impersonation, and targeted phishing.
The Department of Finance said a "limited" number of credit unions had been affected by the potential breach, while credit unions were told that it is not thought that credit union members' accounts and balances had been compromised.
The Central Bank and finance minister Simon Harris have urged credit unions to engage with members about their concerns.
Wellington IT (WIT), a Belfast company which provides software and other services to 50 credit unions, 43 of which are in Ireland, issued correspondence on Monday to notify credit unions using its system of a potential data breach.
It said an automated script that made five million requests was used to exploit a vulnerability, or an "authorisation flaw", on its platform between October 2 and 4.
The "malicious" requests came from an automated client using a valid member login, and the "bad actor" was able to access saved payee records, it said.
"The logs that would identify which members were requested or what each response contained are not available," it said in its correspondence on Monday.
"We cannot therefore, at this stage, confirm which individual records were retrieved and are treating all saved payee records on the platform during this period as potentially affected."
The company said it would provide figures on the number of people affected "as soon as possible".
The potential payee details that could be affected include IBANs, BICs, bank account numbers, sort codes, and full addresses; credit union members' account and balance details "were not retrieved", according to Monday's correspondence.
WIT said it was notified by a credit union last Friday that extortion emails had been sent to it and several credit unions.
"These had been filtered to junk mail and had not been seen by WIT before then," it said.
Read More
It said its initial investigation into the October incident concluded there was "no exposure", but on Sunday morning its engineering team concluded that "saved payee data linked to a member may have been retrieved".
The Irish League of Credit Unions stressed that it is not thought that accounts had been affected and said the incident was still being investigated.
"We understand that the relevant vulnerability has been closed and that member accounts and balances have not been compromised," it said.
A Central Bank spokesman said credit unions had notified it of the suspected breach and urged them to "communicate clearly with their members and inform potentially affected members without undue delay".
"In the first instance, credit union members should contact their credit union with any concerns they may have."
The Department of Finance said it is liaising with the Central Bank and is awaiting further information about the nature and extent of the incident.
The Tánaiste said that any suspected breach of credit union members' data was "deeply concerning".
"My officials will continue to liaise with the Central Bank of Ireland, and other relevant stakeholders to support the affected credit unions in resolution of this issue," the finance minister said.
“I have no doubt in the meantime, credit unions will engage with individual members who will naturally be concerned by this suspected breach.”
BLACK FRIDAY
Already a subscriber? Sign in

CONNECT WITH US TODAY


Be the first to know the latest news and updates